DevOps & Cloud
Engineering
We engineer production-grade AWS infrastructure, Kubernetes platforms and CI/CD pipelines for fintech, healthcare and high-scale SaaS — built to stay up, stay secure, and stay auditable.
 AWS
 Kubernetes
 Terraform
 ArgoCD
 Docker
 Istio
What We Do
Direct technical execution across production cloud environments. Six core engineering capabilities, zero filler.
DevOps & CI/CD Automation
End-to-end CI/CD pipelines and GitOps workflows with built-in SAST, container image scanning, approval gates and automated rollbacks — shipping code from commit to production safely and repeatably.
AWS Cloud Infrastructure
AWS Well-Architected foundations: multi-account landing zones, VPC design, Transit Gateway routing, and HIPAA / PCI-DSS aligned account segmentation for regulated and high-scale environments.
Kubernetes & Platform Engineering
Production-grade Amazon EKS clusters hardened to CIS Kubernetes Benchmark, managed with Helm and ArgoCD, secured with Istio mTLS, and auto-scaled with KEDA for mission-critical workloads.
Cloud Security & Compliance
Zero-trust IAM, KMS envelope encryption, Kyverno policy-as-code, and network isolation — continuously validated against CIS Benchmarks, HIPAA Security Rule, SOC 2 Type II, ISO 27001, HITRUST CSF and PCI-DSS.
Observability & Site Reliability
Unified Grafana LGTM stack — metrics, logs and distributed traces — with SLO-based alerting, automated incident response runbooks, and full audit trail retention for compliance reporting.
Infrastructure as Code
Terraform, OpenTofu and Terragrunt modules with remote state, automated drift detection, and integrated tfsec / Checkov policy scans on every pull request — zero manual changes in production.
How We Engineer
A disciplined, production-grade delivery lifecycle built on immutability, automated validation, and continuous telemetry.
Assess
Audit your cloud environment against CIS Benchmarks, HIPAA Security Rule controls, SOC 2 criteria, cost leakage, and CI/CD bottlenecks to establish a clear remediation baseline.
Design
Architect a scalable, immutable infrastructure blueprint aligned with AWS Well-Architected pillars, HIPAA account segmentation, and applicable regulatory frameworks.
Automate
Codify every resource with Terraform or OpenTofu, with SAST, tfsec and policy scans embedded in each pipeline — no manual console actions, ever.
Secure
Enforce least-privilege IAM, KMS encryption, Kyverno admission policies, automated secrets rotation, and mTLS — mapped to HIPAA, PCI-DSS or SOC 2 control requirements.
Deploy
Ship with confidence via automated rolling deployments and canary rollouts, using Cosign-signed and vulnerability-scanned container images only.
Observe
Correlate logs, metrics and traces in Grafana LGTM, retain immutable audit trails for compliance evidence, and alert on SLO budget burns before users notice.
Optimise
Continuously right-size resources, rotate spot pools, tune latency budgets, and re-run compliance audits to close configuration drift before it becomes a finding.
Production Cloud Blueprint
Explore our hardened reference architecture: zero-trust network segmentation, isolated Kubernetes node pools, and audited GitOps synchronization.
Tier 1: Public DMZ & Edge Routing
Inbound HTTPS traffic is scrubbed by Cloudflare DDoS protection, validated against AWS WAF Managed Rule sets (OWASP Top 10, Bot Control), and TLS 1.3 terminated at Application Load Balancers before any workload contact.
- AWS WAF Rate Limiting, Bot Control & geo-blocking rules
- Multi-AZ highly available NAT Gateways with egress domain filtering
- VPC Flow Logs streamed to S3 for HIPAA §164.312(b) audit retention
Verified Engineering Outcomes
Explore deep technical breakdowns of high-scale Kubernetes migrations, zero-trust security hardening, and multi-region infrastructure.
Zero-Downtime Multi-Region EKS Migration for a Fintech Platform
Migrated a PCI-DSS scoped, multi-tenant fintech microservice platform from legacy EC2 instances to Amazon EKS 1.30 across two AWS regions — achieving 99.99% uptime and 38% lower compute spend with zero data loss.
- Dual-region active-passive failover with Route 53 latency-based routing and automated health checks
- Karpenter spot node orchestration with graceful drain, reducing node warm-up from 8 min to under 60s
- Stateful Aurora Multi-Region Global DB cutover with zero data loss and sub-30s automatic failover
HIPAA-Aligned Zero-Trust Kubernetes Hardening for a Healthcare SaaS
Hardened a healthcare SaaS Kubernetes environment to meet HIPAA Security Rule and HITRUST CSF requirements — implementing zero-trust network policies, mutual TLS, admission control, and centralized PHI-access audit logging.
- Kyverno validating webhooks enforcing non-root pod execution, Cosign image signatures and HIPAA-required resource labelling
- Istio PeerAuthentication in STRICT mode with AuthorizationPolicies governing PHI-adjacent service communication
- Centralized PHI access audit trail via Falco + CloudTrail, providing HIPAA §164.312(b) compliant audit controls
SOC 2-Ready Multi-Account AWS Platform via Terraform & Transit Gateway
Designed and delivered an automated multi-account AWS Organisation with 8 isolated environments, centralised egress inspection, federated IAM, and continuous SOC 2 control evidence collection — provisioned in under 2 hours from scratch.
- Terraform & Terragrunt modular state architecture with remote S3 locking and per-account blast radius isolation
- AWS Transit Gateway hub routing all inter-account traffic through a dedicated security inspection VPC with Network Firewall rules
- Automated SOC 2 evidence collection via AWS Config conformance packs, CloudTrail, GuardDuty and Security Hub findings
Battle-Tested Technologies
We build exclusively with proven open-source and cloud-native standards. Every tool in our stack has operated under production load.
Cloud & Infrastructure
Kubernetes & Platform
CI/CD & Delivery

Observability & SRE
Containers & Runtimes
Security & Compliance


Measurable Reliability
We measure engineering success through uptime, security enforcement, deployment velocity, and infrastructure repeatability.
Behind Devistio
Devistio is an engineering-first AWS DevOps and cloud infrastructure consultancy founded by Talha Rehman — delivering Kubernetes platforms, CI/CD automation, security hardening and compliance-ready architectures for fintech, healthcare and high-scale SaaS teams.
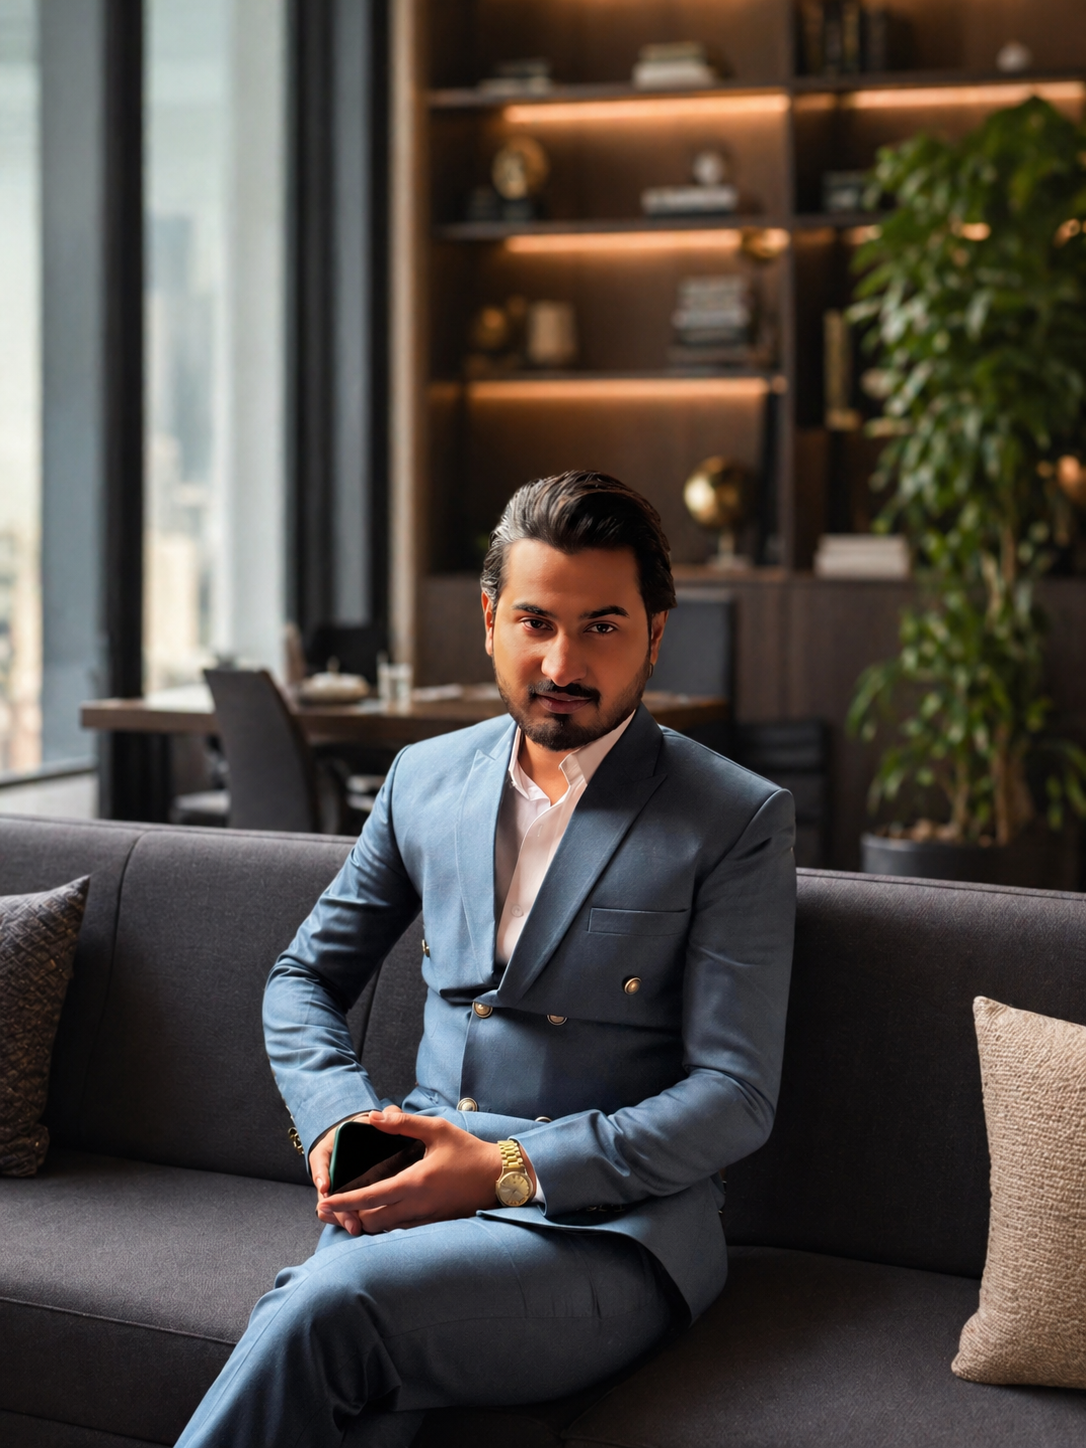
Hands-on AWS and Kubernetes engineer with deep expertise in multi-account cloud architectures, HIPAA and SOC 2-aligned security hardening, GitOps delivery pipelines, and high-reliability Site Reliability Engineering (SRE) for regulated industries.


Let's Build Your Infrastructure
Direct access to cloud & platform engineering expertise. No sales overhead, no junior handoffs.